Account takeover prevention software detects or blocks unauthorized account access, including when the attacker holds valid stolen credentials. The category spans identity and MFA providers, fraud suites, behavioral biometrics, bot management, and browser-layer fingerprinting. Most teams run two or three of these layers and wire them together, because each one watches a different moment of the session.
TL;DR: account takeover prevention software
- Three layers, three jobs: Identity and MFA (Okta, Microsoft Entra ID Protection) prove who is logging in. Fraud suites (Sift, Forter) and behavioral biometrics (BioCatch) score what the account does. Browser and bot tools (cside, Castle, DataDome, Cloudflare, HUMAN) judge whether the session itself is human and trusted.
- MFA is a floor: Stolen session tokens and adversary-in-the-middle (AiTM) phishing get past a second factor. The 2022 Crypto.com breach bypassed 2FA and took more than $30 million from 483 accounts.
- The shortlist: cside for raw device and browser signals in your own rules, Castle for web plus mobile apps, BioCatch for banking, Sift or Forter for a managed fraud suite, and DataDome, Cloudflare, or HUMAN for bot traffic at scale.
Short on time? See how cside's account takeover protection adds browser and device intelligence to an existing ATO prevention stack.
New to account takeover? Start with what account takeover (ATO) is.
How we evaluated these tools
Account takeover has several entry points across the login flow. So this guide sorts tools by the stage of the attack chain they actually defend: credential validation (credential stuffing and bot-driven login testing), account access, session persistence, and monetization. Within each layer, we compared how a tool delivers its signal (raw data you act on, or a fixed score) and how transparent its pricing is.
This guide is designed to help fraud and executive teams build a stack that prevents fraudulent chargebacks and protects their users. The losses are large: according to PaymentsJournal, account takeover fraud cost consumers $15.6 billion in 2024, up from $12.7 billion the year before.
Compare ATO prevention by defense layer
Comparisons that stack identity, fraud suite, and browser tools in one table hide the real question: which layer are you missing? An MFA provider, a fraud suite, and a browser-layer tool do three different jobs at three different moments in the session.
| Defense layer | What it proves | When it acts | Blind spot it leaves |
|---|---|---|---|
| Identity / MFA | Who is authenticating | At login, before the session | Session theft and AiTM after the factor passes |
| Fraud suite | Whether the account's actions look risky | After login, at the transaction | Automated or hijacked sessions that act "normal" until payout |
| Browser + bot | Whether the session itself is human and trusted | In the page, during the session | Server-side identity policy and cross-merchant transaction history |
Read the table by its last column. Each layer's weakness is another layer's reason to exist. Buy to close the blind spot you actually have, not to collect the longest feature list.
Types of account takeover prevention software
| Category | What it does | ATO stages covered | Example vendors |
|---|---|---|---|
| Full anti-fraud suites | Combine account, transaction, behavioral, and fraud-risk signals | Login, post-login, transaction | Sift, Forter |
| Fingerprinting solutions | Identify devices, browsers, network risk, and session anomalies | Pre-login, login, in-session | cside, Castle |
| Behavioral biometrics | Score how a user types, moves, and handles the device | Login, in-session | BioCatch |
| MFA and identity | Second-factor and risk-based authentication at login | Account access | Okta, Microsoft Entra ID Protection |
| WAFs and bot management | Network-layer protection, rate limiting, bot scoring | Credential validation | Cloudflare, DataDome, HUMAN Security |
Full anti-fraud suites
Full anti-fraud suites aim to be all-in-one platforms that cover payment fraud, account takeover, and fake accounts, and some extend into AML compliance and KYC verification. They are powerful, but they are priced for enterprise budgets and take ongoing tuning to keep false positives down.
Sift and Forter are examples. They analyze transaction data, monitor post-login behavior, and use machine learning trained on cross-merchant fraud data. Most also bake some form of device fingerprinting into the risk score.
Fingerprinting solutions
Fingerprinting solutions collect device and browser-level data. When the fingerprint on a new login does not match the account's baseline, and other signals agree, that is a strong indicator that a takeover is in progress or complete.
Platforms like cside detect new devices, impossible travel, VPN and proxy use, and fingerprint mismatches. They then feed those signals into enforcement such as step-up MFA or risk scoring.
Browser-layer signals to watch, none of which a server-side score can see on its own:
navigator.webdriverand automation flags: the property browsers expose when a session is driven by WebDriver or CDP, plus the residual traces stealth plugins try to patch and miss.- CDP and runtime leaks: Chrome DevTools Protocol activity and
Runtimeartifacts that betray a headless or remotely driven browser even when the user agent looks ordinary. - Fingerprint drift: the same account presenting inconsistent or rotating device fingerprints across logins, a hallmark of bot farms and shared session-replay tooling.
- Residential-proxy and VPN behavior: signals that an otherwise clean residential IP is being used to launder automated traffic, beyond what an IP blocklist can tell you.
- Malicious in-page scripts: credential-harvesting overlays or AiTM redirect logic injected through third- or first-party scripts, visible at runtime on the page where the user would be phished.
MFA and identity solutions
MFA solutions add a second verification step to the login itself. They do not detect fraud or analyze device data on their own. They make it harder to authenticate with stolen credentials in the first place.
Okta requires a second factor before granting access and can step up verification when a login looks unusual. Microsoft Entra ID Protection scores sign-in risk and hands it to Conditional Access, which can then require MFA or block the sign-in. Traditional MFA is increasingly bypassed by new attack playbooks: authentication vendor MojoAuth reported blocking 4.2 billion authentication attack attempts on its platform in 2025, with session hijacking up 127% year over year.
Adjacent solutions
WAFs like Cloudflare and AWS WAF protect against broad web attacks and add basic rate limiting on login endpoints. A base WAF rule set judges requests by IP, headers, paths, and request rates rather than device or in-page behavior, so it catches simple brute force but misses credential stuffing spread across thousands of IPs. Both vendors sell add-ons that go further: Cloudflare Bot Management, and the account takeover prevention rule group in AWS WAF Fraud Control.
Bot management platforms like DataDome and HUMAN Security separate human traffic from automated traffic. They use challenges and behavioral analysis to stop high-volume credential stuffing, and AI-driven bots built to mimic human behavior keep raising the bar for every vendor in the category.
Upstream credential intelligence services round out the picture. They monitor dark web markets and infostealer logs for stolen credentials that belong to your users, and they are purely preventive.
How to buy across the three layers
Do not buy the longest checklist. Buy the layer your attack path leaves open.
- Map your path. Write out login, validation, access, session persistence, and monetization, then mark which layer watches each step.
- Find the single point of failure. If MFA is your primary ATO control, ask what happens after authentication. If a fraud platform only evaluates transactions, ask what happens before a suspicious transaction reaches it.
- Avoid duplicate signals with no shared action. Two tools both flagging "new device" add little if neither signal changes the decision.
- Run a real proof. Replay historical incidents through the candidate layer and check whether it would have flagged the suspicious session, not only the transaction.
- Wire the handoff. A browser-layer flag should trigger step-up MFA at your identity provider or feed a risk score at your fraud suite. Send it through an API or webhook so each layer acts on the others' evidence.
The 10 best account takeover fraud prevention tools, reviewed
The tools below cover different parts of the ATO prevention stack, and the right fit depends on the layer you need to strengthen. Pricing reflects what each vendor publishes as of October 2026.
| Tool | Defense layer | Best for | Published pricing |
|---|---|---|---|
| cside | Browser and device intelligence | Raw device and browser signals in your own auth or fraud rules | Free up to 1,000 API calls/month; Business $99/month |
| Castle | Fingerprinting and risk scoring | One platform across web and native mobile apps | Free; Pro $200/month; Enterprise from $4,000/month |
| BioCatch | Behavioral biometrics | Banks scoring behavior through the whole session | Not published |
| Okta | Identity and MFA | ATO controls inside a broader identity program | Workforce Identity from $6/user/month, $1,500 annual minimum |
| Microsoft Entra ID Protection | Identity and MFA | Organizations already on Microsoft 365 or Azure | Included in Entra ID P2 ($10/user/month) and Entra Suite ($12/user/month) |
| Sift | Fraud suite | Fraud ops teams scoring ATO, payments, and fake accounts in one place | Not published |
| Forter | Fraud suite | E-commerce and loyalty-heavy merchants | Not published |
| DataDome | Bot management | Low-friction bot defense at enterprise scale | Bot Protect from $3,830/month |
| Cloudflare Bot Management | WAF and bot management | Sites already on a Cloudflare Enterprise plan | Enterprise add-on, quote only |
| HUMAN Security | Bot management | Credential stuffing defense at enterprise scale | Not published |
1. cside

Many security teams need more visibility into the session itself. cside closes that gap with browser and device intelligence. Its device intelligence product collects 250+ device, network, and behavioral signals per session, covering device fingerprinting, VPN and proxy detection, automation signals, and AI agent detection. Those signals feed your own enforcement logic through an API and webhooks.
Key features:
- Device fingerprinting: a persistent device ID built from 250+ signals (IP, geolocation, VPN and proxy detection, browser, OS, screen, and more), so a login from an unrecognized device stands out even when the password is correct.
- ATO signals: impossible travel, unknown devices, and one device accessing many accounts, available as raw signals or through pre-built alert templates for high-risk patterns.
- Bot and AI agent detection: flags headless browsers, automation frameworks, and AI agents that try to pass as human during credential stuffing.
- Enforcement you control: send a flag to step-up MFA, a block, or a review queue, using thresholds you define.
- Script monitoring: cside's client-side security product watches the scripts on your pages for credential-harvesting overlays and phishing redirects.
- Mobile apps: native iOS and Android SDKs, in beta (talk to us for access), bring the same 250+ signals as the web client into apps, plus app-only signals such as jailbreak, root, and emulator detection.
Reviews:
- 4.9/5 on SourceForge (37 reviews and ratings shown: 25 native SourceForge reviews plus 12 verified third-party ratings surfaced there).
- 4.8/5 on G2.
Pricing (device intelligence): free up to 1,000 API calls per month; Business is $99/month for 50,000 calls with a 14-day free trial; Enterprise is custom.
Choose cside when you want first-party device and browser signals that you can feed into your existing authentication or fraud workflow.
2. Castle
Castle combines device fingerprinting with behavioral and account-risk signals. According to Castle's documentation, it returns three scores per event (Account Takeover, Bot, and Account Abuse, shown as 0–100 in the dashboard), and no-code dashboard policies turn those scores into allow, challenge, or deny responses. Castle ships mobile SDKs for iOS, Android, React Native, and Flutter, and its signal set flags rooted or jailbroken devices and emulators.
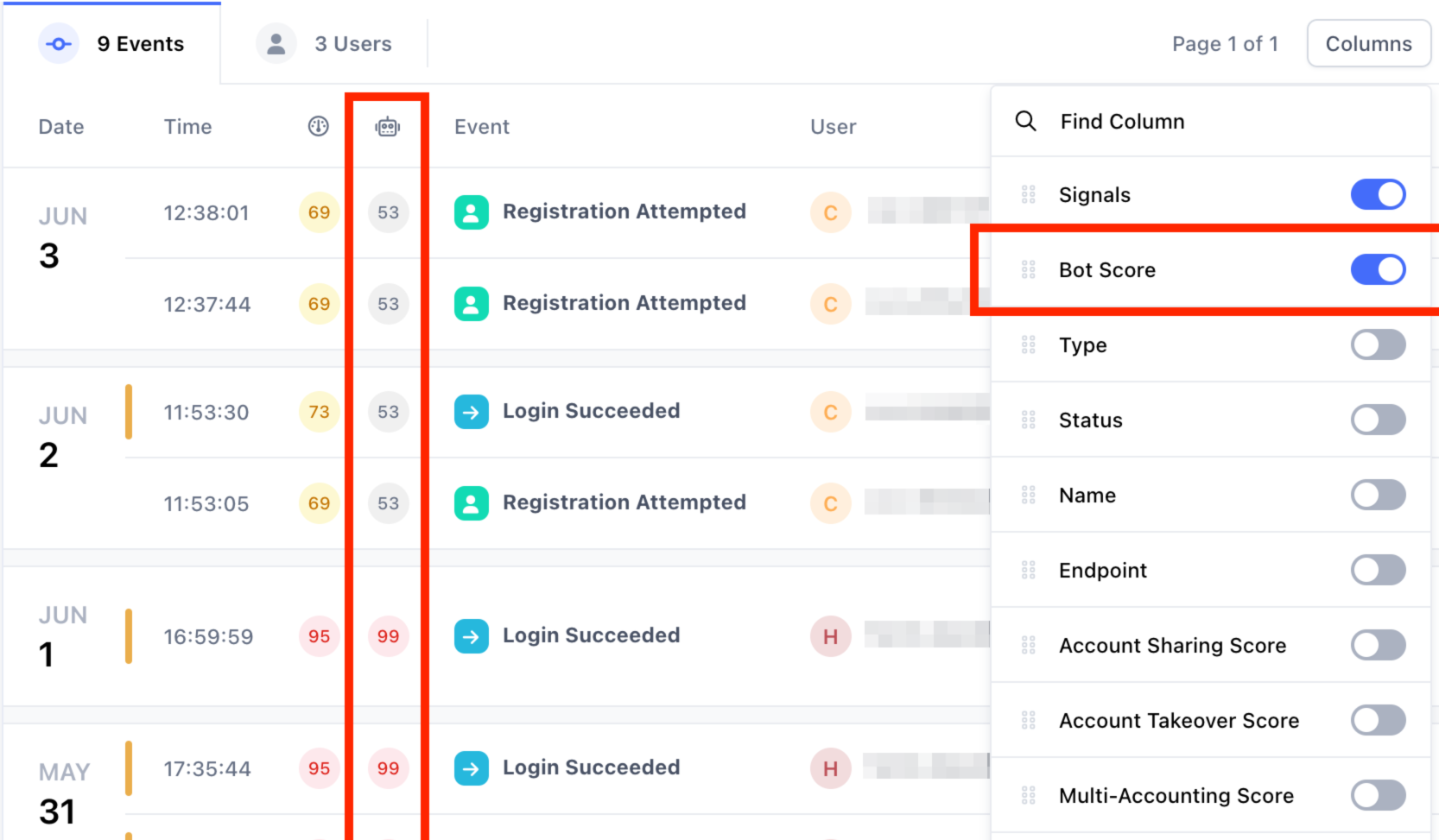
Source: docs.castle.io
Pricing: free plan; Pro at $200/month; Enterprise from $4,000/month.
Choose Castle when you need web and mobile app coverage in one platform, including React Native or Flutter apps. Head-to-head: Castle vs cside.
3. BioCatch
BioCatch reads how a user behaves rather than what they know or hold. Throughout the session, it tracks signals such as keystroke rhythm, mouse movement, touch gestures, and device-handling patterns. BioCatch is a long-standing name in banking-grade fraud prevention. In August 2026, Visa agreed to acquire the company for $2.4 billion in cash; per BioCatch's announcement, the deal is pending regulatory approval and expected to close by the end of Visa's fiscal second quarter of 2027. That price tag shows how seriously the payments industry takes behavioral biometrics for ATO.
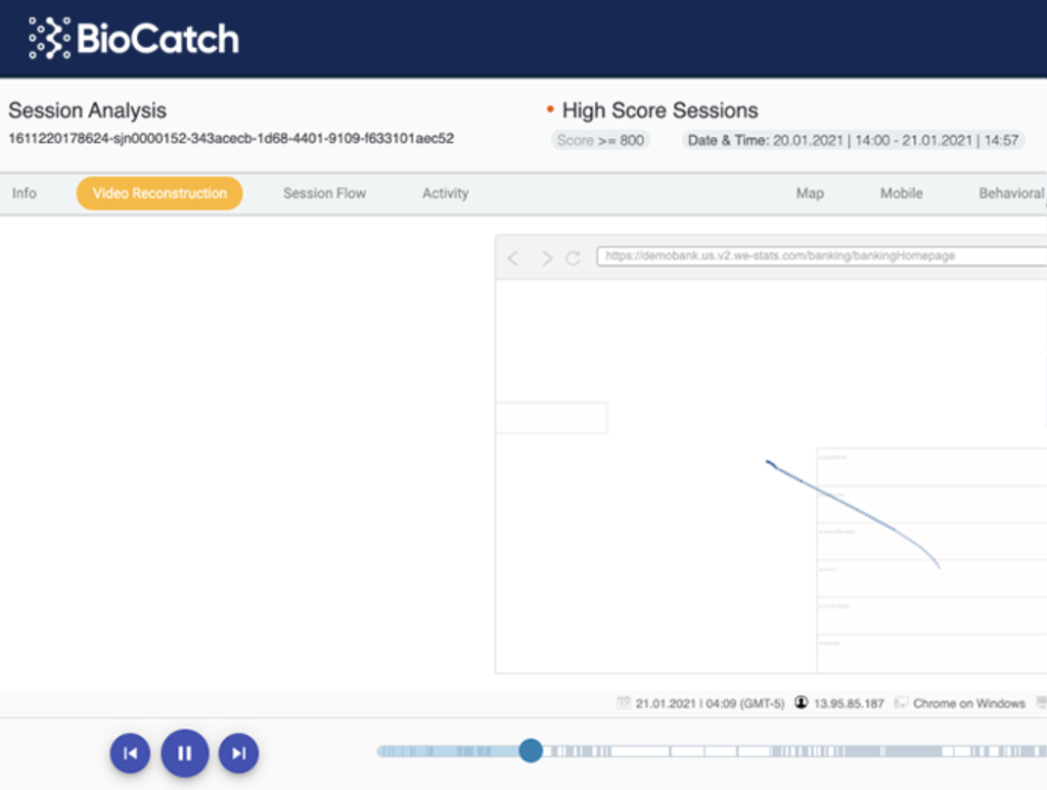
Source: biocatch.com
Choose BioCatch when your primary use case is banking or financial services and continuous behavioral risk scoring matters more than a device fingerprint alone.
4. Okta
Okta provides identity and access management. Adaptive MFA weighs device, network, location, and behavior context to decide when authentication should be strengthened, and the Identity Threat Protection add-on keeps assessing risk during the session, for example to catch session hijacking. Okta also supports SSO, lifecycle management, Okta FastPass, and FIDO2 WebAuthn authenticators. For customer-facing logins, Auth0 (Okta's customer identity platform) adds Attack Protection: bot detection, suspicious IP throttling, brute-force protection, and breached password detection.
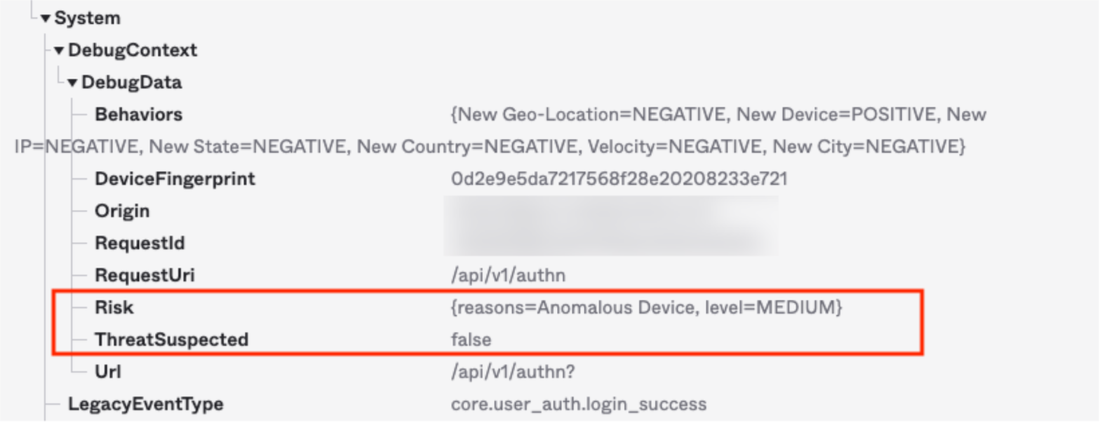
Source: help.okta.com
Pricing: Workforce Identity suites start at $6/user/month (Starter, which includes MFA) with a $1,500 annual contract minimum. Adaptive MFA is included from the Essentials suite, and Identity Threat Protection is an add-on.
Choose Okta when ATO prevention is part of a broader identity program and you need authentication, access management, and risk-based controls in the same ecosystem.
5. Microsoft Entra ID Protection
Microsoft says Entra ID Protection draws on trillions of signals across its security products. It turns that scale into risk-based Conditional Access, flagging risks like leaked credentials, password spray, and token replay. Microsoft is also extending these risk-based policies to AI agent identities, alongside the Microsoft Entra Agent ID preview.
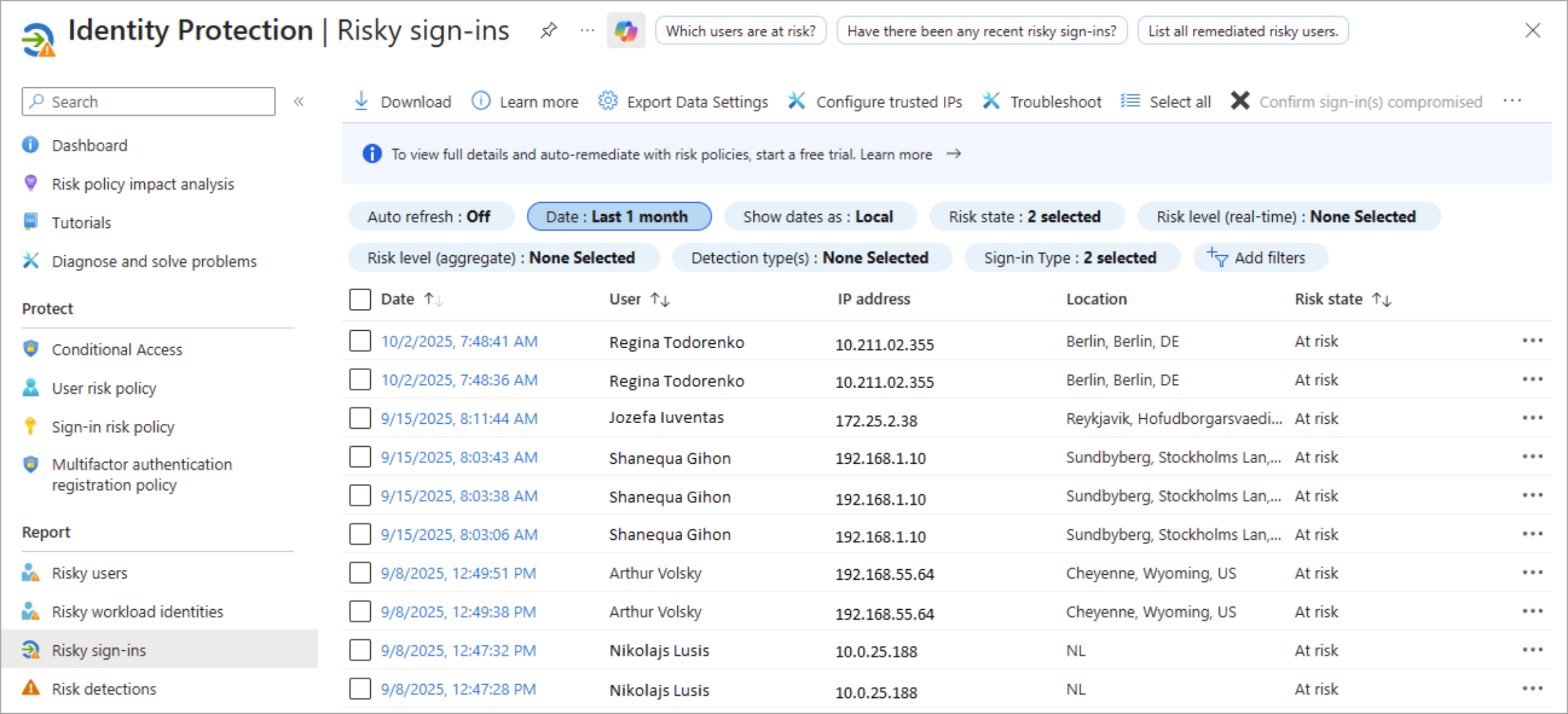
Source: learn.microsoft.com
Pricing: included in Microsoft Entra ID P2 ($10/user/month), Microsoft Entra Suite ($12/user/month), and Microsoft 365 E5.
Choose Microsoft Entra ID Protection when your organization already runs on Microsoft 365 or Azure and wants identity risk protection inside licensing it may already hold.
6. Sift
Sift is a full anti-fraud suite that covers account takeover, payment fraud, and fake accounts. The platform scores logins, signups, and transactions using machine learning trained across its network, which Sift says processes more than 1 trillion events a year from 700,000+ sites and apps. So a user who is new to you is often already known to Sift.
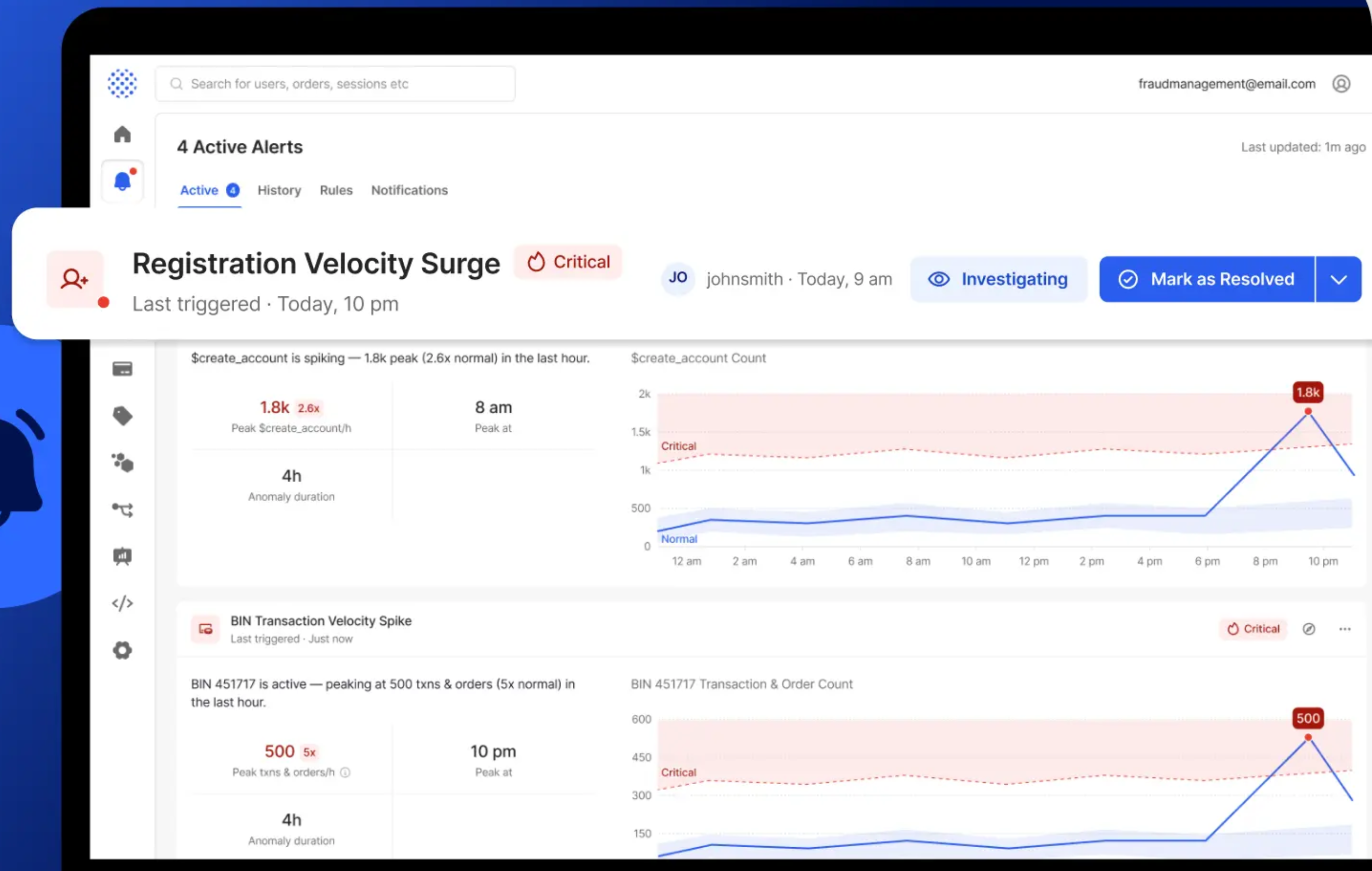
Source: sift.com
Pricing: not published; Sift quotes custom contracts.
Choose Sift when you have a dedicated fraud ops team and want ATO, payment fraud, and fake-account scoring in one platform. Head-to-head: Sift vs cside.
7. Forter
Forter's Account Protection product is built to stop account takeover attempts across high-risk account actions. It also targets fake account creation and incentive abuse, and protects loyalty rewards and stored value. These features are part of a broader platform that also covers fraud management, payment optimization, dispute management, and abuse prevention. Forter does not publish pricing; buyer data from Vendr indicates contracts are usually tied to GMV or approved transaction volume rather than a flat fee.
Choose Forter when you're an e-commerce or loyalty-heavy business that wants identity protection with payment optimization and dispute management. Head-to-head: Forter vs cside.
8. DataDome
DataDome was named a Leader in The Forrester Wave: Bot and Agent Trust Management Software, Q2 2026. Its Device Check is an invisible challenge: it validates device signals in the background with no checkbox, puzzle, or other user interaction. DataDome's separate slider CAPTCHA covers the cases where a visible challenge is needed. DataDome publishes its pricing: Bot Protect starts at $3,830/month on the Essentials tier, and its Account Protect product is priced by monthly event volume.
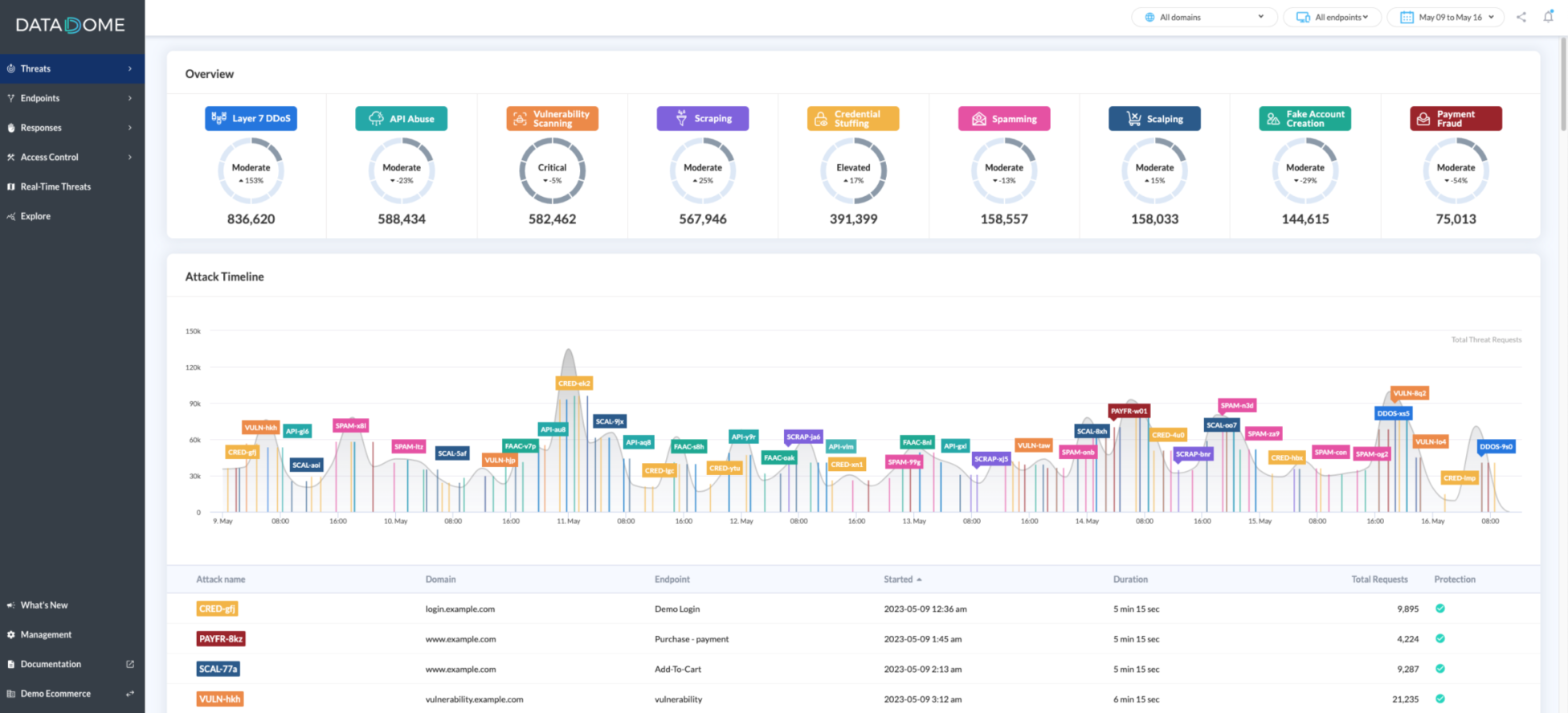
Source: docs.datadome.co
Choose DataDome when you want enterprise-grade bot detection built around minimizing friction for legitimate users. Head-to-head: DataDome vs cside.
9. Cloudflare Bot Management
Cloudflare Bot Management runs on the same network as Cloudflare's WAF, CDN, and DDoS protection. Cloudflare trains its machine learning models on traffic from a large share of the internet and positions the product to protect login endpoints from credential stuffing. Every request gets a bot score you can act on in custom rules. Bot Management is an add-on to Cloudflare Enterprise plans.
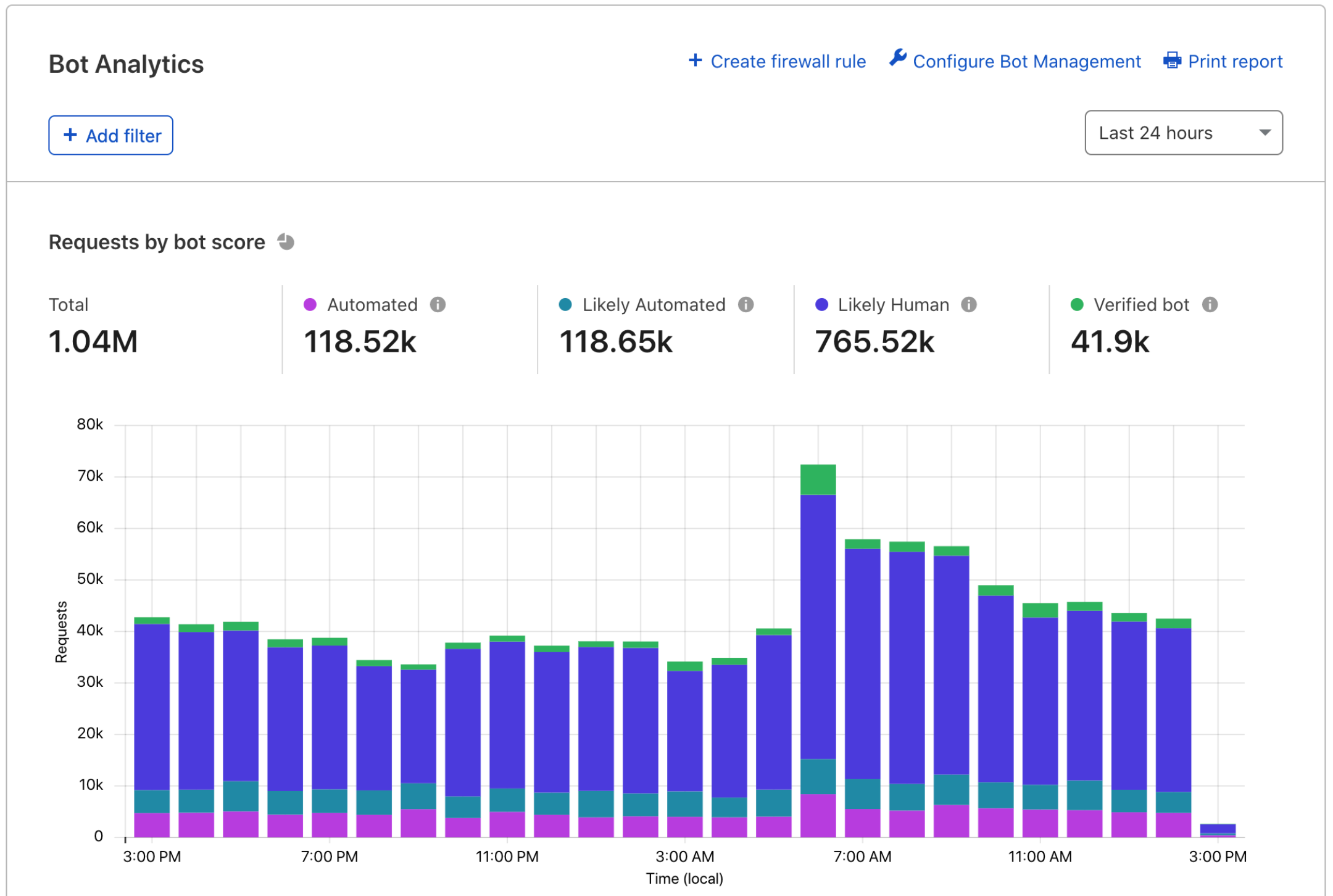
Source: developers.cloudflare.com
Choose Cloudflare Bot Management when your infrastructure already runs through Cloudflare on an Enterprise plan and you want bot defense as one more layer of that contract.
10. HUMAN Security
HUMAN merged with PerimeterX in 2022, and the combined company runs under the HUMAN brand. Its account takeover defense blocks automated credential stuffing and brute force at login, neutralizes compromised credentials, and assesses activity inside the account across web, mobile, and API traffic. It can integrate at your edge, such as a CDN, and pricing is sales-led with no published rates.
Source: docs.humansecurity.com
Choose HUMAN Security when account takeover and credential stuffing are your dominant threat and you have the budget for an enterprise engagement. Head-to-head: HUMAN Security vs cside.
Where new account fraud fits
Account takeover targets accounts that already exist. New account fraud is the upstream half of the same problem: attackers register accounts at scale for trial abuse, promo abuse, and multi-accounting, then use them the way they would use stolen ones.
Several tools above cover both. Sift and Forter score fake account creation alongside ATO, Castle's Account Abuse score covers fake accounts and multi-accounting, and device fingerprinting links the many "new" accounts that come from one device. cside adds Signup Shield, which turns each registration into a real-time trust verdict using email, domain, behavioral, and cross-tenant signals. For the full breakdown, see what new account fraud is and how detection works.
What's changing in 2026
ATO-related chargebacks cost merchants an average of $576 per incident, against $271 for a typical chargeback, according to Equifax's analysis of its 2020 to 2023 transaction data. Merchants have very little defense once a takeover has already produced a genuine-looking fraudulent transaction. The only real prevention mechanism is stopping the takeover before it happens.
MFA was a strong defense for years and is still a foundational layer, but sophisticated attacks now go around it. A well-known example is the Crypto.com breach of January 2022, where attackers bypassed the exchange's two-factor authentication and withdrew more than $30 million from 483 customer accounts.
One pattern that defeats MFA starts on the page itself. Attackers inject a CSS overlay or a script into a legitimate site that sends users to a fake login page identical to the real one. An adversary-in-the-middle (AiTM) proxy relays the login to the real site in real time, so the user enters their password and MFA code normally. The proxy then captures the session token issued after authentication and uses it to walk into the account.
Page injection at this scale is well documented. cside's Q1 2025 client-side attack recap found nearly 300,000 compromised websites in that quarter alone, including one campaign that pushed full-screen overlays onto more than 35,000 sites.
Automation tooling is the second trend growing in 2026. In cside's research report on the future of web security, legacy bot detection tools failed 81% of cside's test attempts, and "user-action" AI bots, which act on pages for a user instead of crawling them, increased 15x in 2025. Fraud suites have little visibility into this tooling because it impersonates a normal browser right up to the payout moment, when an ML score arrives too late. Browser-layer detection sees the automation in the session, before it reaches the transaction.
Reduce account takeover attacks with cside
Account takeover prevention works best when the controls you already have can see the signals they need to make a decision. cside gives you device intelligence and browser-level signals to detect compromised sessions before they cause damage.
See how cside's account takeover protection maps to your login flow, then start with a free plan or book a demo to see how fingerprinting fits into your ATO prevention stack.