What's new?
CSP Builder turns the script hosts cside already observes on your site into a Content-Security-Policy you can deploy.

Pick a domain and you get a suggested policy across seven directives: script-src, connect-src, img-src, style-src, frame-src, font-src and media-src. Every host we observed is listed and grouped by what we know about it, so you can switch off anything that does not belong, add a host we have not seen yet, and restrict everything the policy does not name to your own origin. Copy the report-only header first and watch the violations land in your dashboard, then switch to enforce once it is clean.
CSP Builder is rolling out now. Contact us to enable it for your team.
Some bots go out of their way to look like regular browsers. One common trick is spoofing the browser’s automation properties so they do not give themselves away.
cside now catches this automatically. The signal appears in your fingerprint data, so you get a clearer picture of who is actually visiting your site.
The Fingerprint Dashboard is out of beta and open to all customers.
You can now monitor device fingerprints across your traffic, filter by AI agent signals to separate automated visitors from real ones, and manage everything from a single view. Usage is tracked and billed alongside your existing cside subscription, so there is nothing extra to set up.
New teams now get a guided setup flow based on what they are actually trying to do.
Whether the goal is PCI compliance, fraud prevention, AI agent detection, or device fingerprinting, onboarding now walks teams through the steps that matter for their situation instead of a generic checklist.
We introduced per-connection features based on JA3/JA4 TLS fingerprinting. By computing the JA4 hash from the full TLS ClientHello (including cipher suites, extensions, ALPN, and elliptic curves), we can now detect VPN client software that attempts to masquerade as a standard web browser.
Linear & Jira Integration
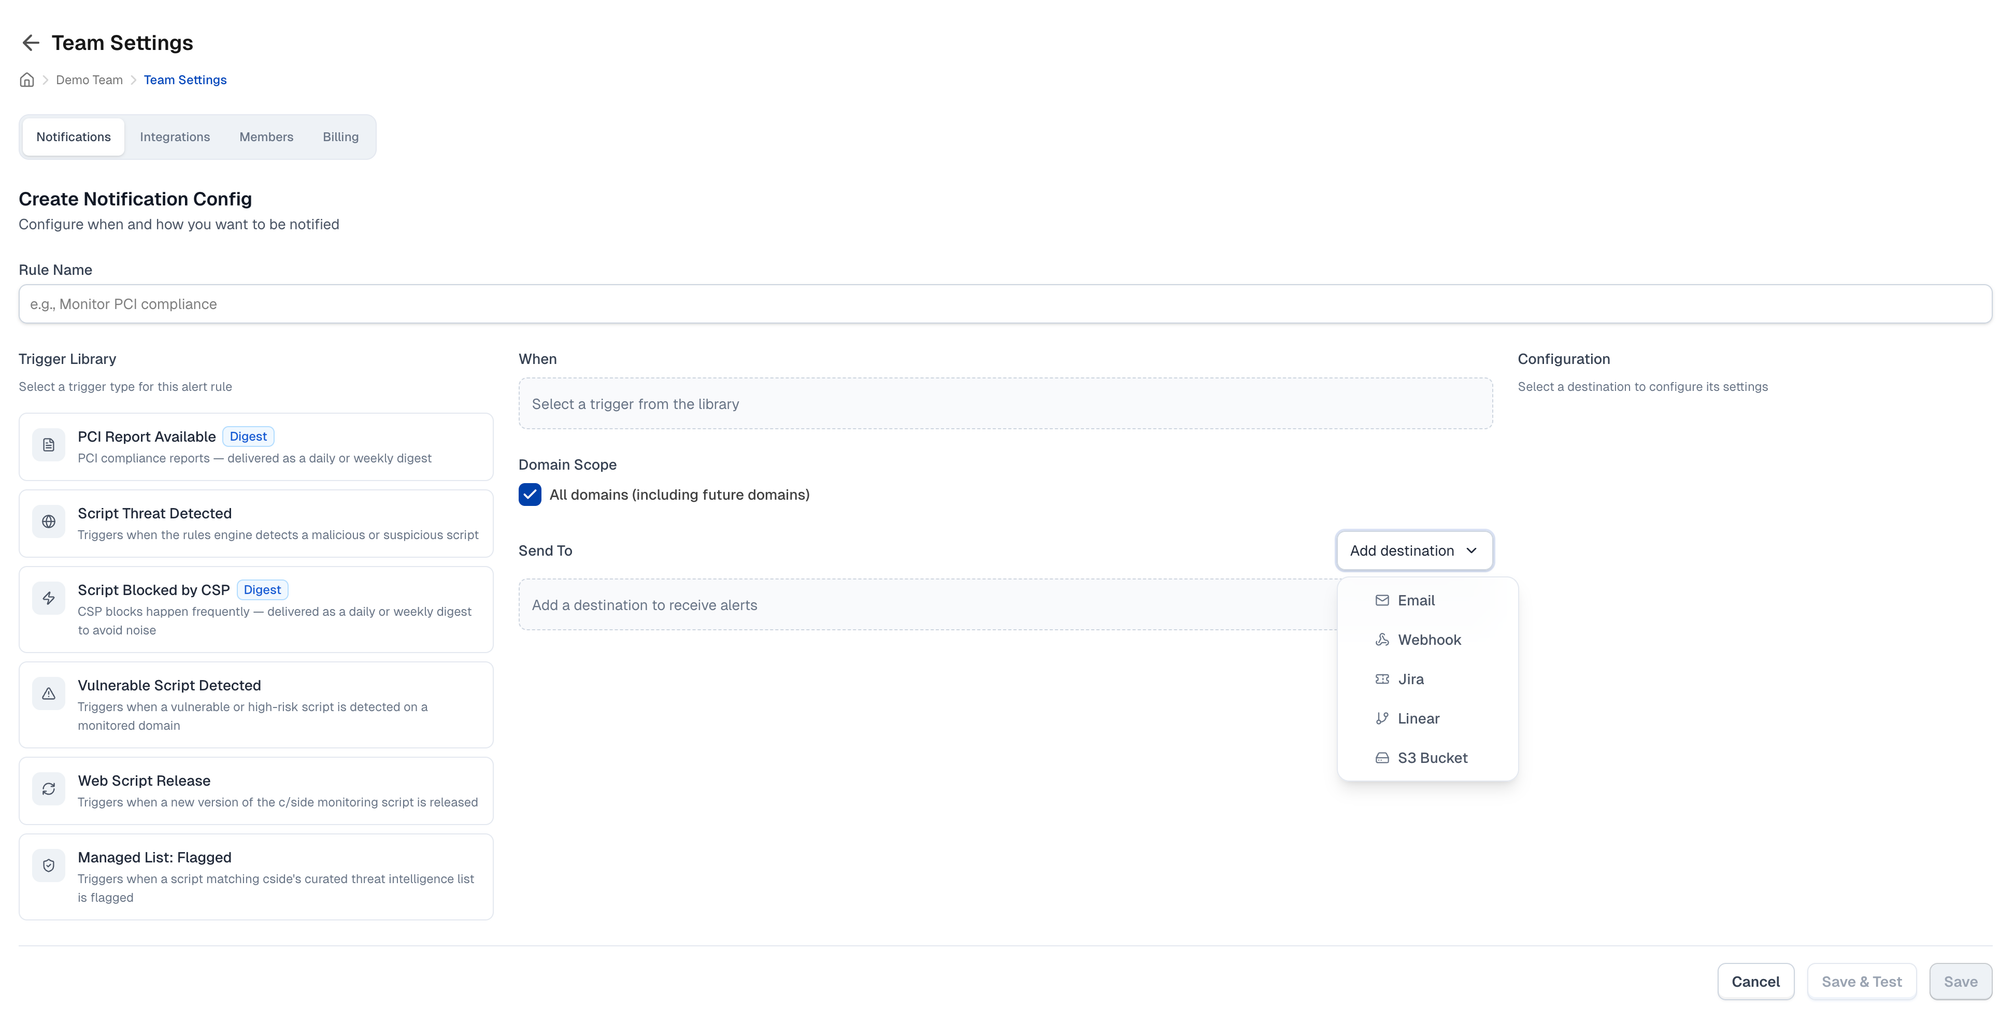
You can now connect cside to Linear and Jira to automatically create issues from any alerts. We’ve reworked how notifications at cside work, so you control which alerts are sent and where. Linear and Jira integrations are available on the Business and Enterprise plan. Check out the docs to get started.
We introduced a self-serve 14-day free trial for all business plan tiers, so new customers can try our premium features before they buy.
We implemented new detections for ad injection via client-side scripts. The system now populates iframe data, resolves iframe URLs, and alerts customers when scripts exhibit suspicious redirect behavior (e.g., 5 or more redirects).
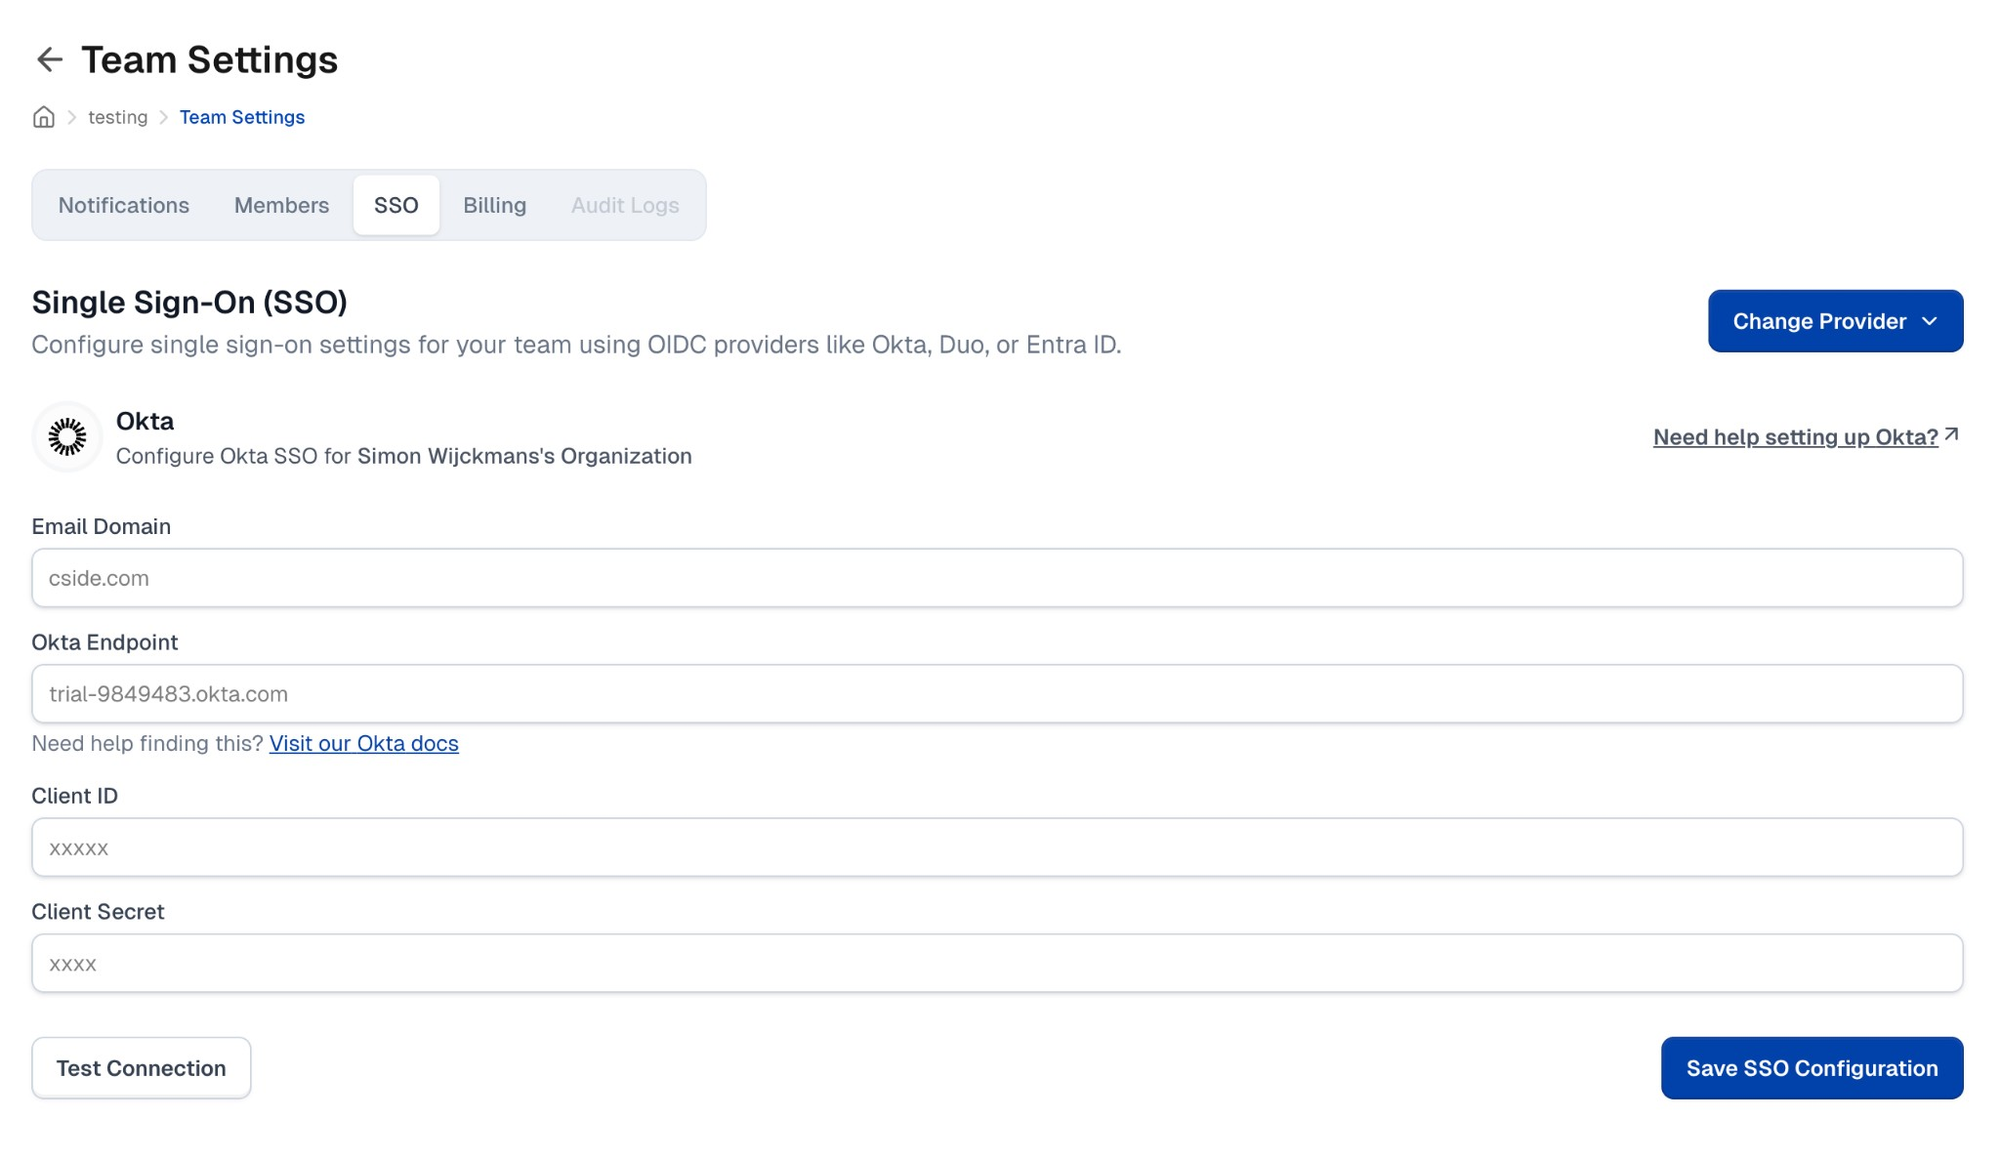
The cside enterprise plan now supports self service SSO setup for Okta, Microsoft Entra ID (formerly Azure AD), and Duo Security.
Configure your identity provider directly in the cside dashboard. No support tickets required. Security teams can onboard faster with full control over authentication settings.
Here’s a very gentle rebrand to cside (at least in copy). Legacy search algorithms struggle to understand special characters and this became an increasingly silly problem. So from now on, it is cside. With the new brand, we’re also pushing a new website, cside.com. Our new website shows the long ongoing effort of cside’s expansion to other client-side security solvable problems. To begin, Chargeback fraud evidence for Compelling Evidence v3, detecting fraudulent applicants as they fill out the job form and various privacy and compliance use-cases.